
Certificate Lifecycle Management: When Scripts Are No Longer Enough
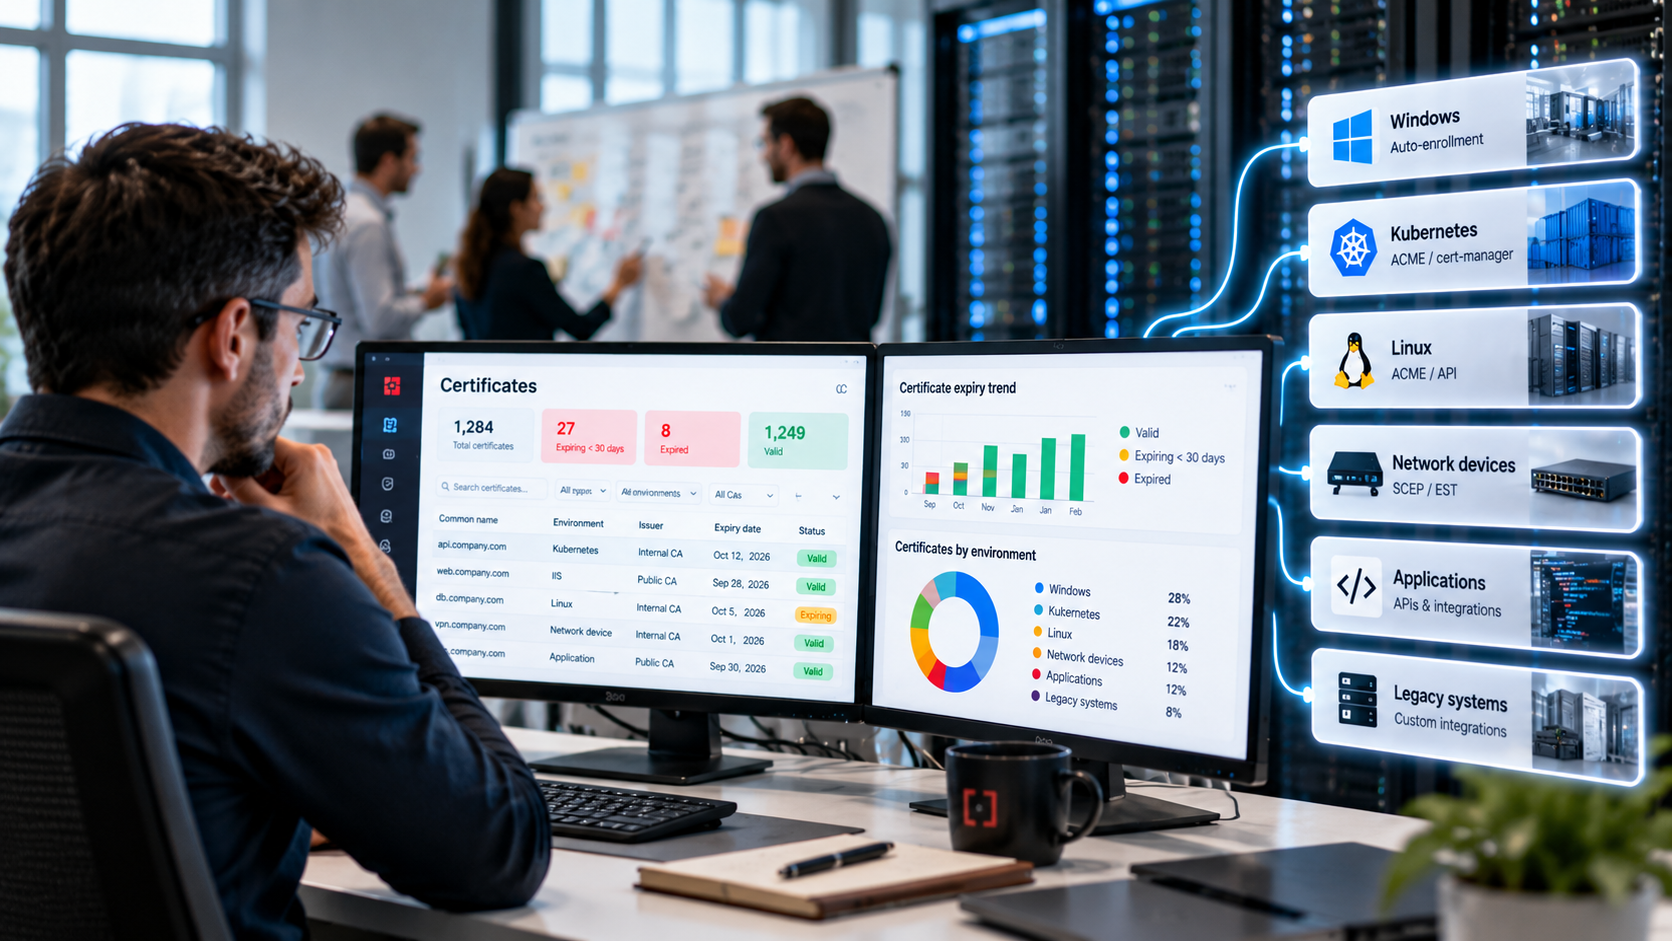
CERTIFICATE LIFECYCLE MANAGEMENT AT A GLANCE
What is Certificate Lifecycle Management?
Certificate Lifecycle Management (CLM) is the structured management of certificates throughout their operational lifecycle.
That includes more than issuing and renewing certificates.
A mature certificate lifecycle can include:
Discovery → Inventory → Enrollment → Deployment → Monitoring → Renewal → Revocation → Reporting
NIST's definition of certificate management similarly extends beyond issuance to include certificate storage, use, monitoring, enrollment, installation and revocation. NIST Computer Security Resource Center
The objective is to ensure that certificates remain:
known, owned, valid, correctly deployed, compliant with policy and replaceable when necessary.
Why do organisations end up managing certificates with scripts?
Almost nobody deliberately designs a certificate-management environment around dozens of scripts.
It happens gradually.
A new system creates a new requirement:
Linux web server → Bash script
Kubernetes → ACME / cert-manager
Network appliance → SCEP or API integration
IIS → Windows enrollment plus deployment/binding automation
Legacy application → custom integration
Each decision may be technically reasonable.
The problem is that each solution typically understands its own certificates, not the complete certificate estate.
Over time, certificate automation can become a collection of independent processes rather than one managed lifecycle.
What is the difference between scripts and Certificate Lifecycle Management?
Why is certificate inventory the foundation of CLM?
Before certificates can be governed or automated, an organisation needs to know what exists.
A useful certificate inventory should answer questions such as:
What certificate is this?
Where is it installed?
Who owns it?
Which CA issued it?
When does it expire?
Which algorithms and key sizes does it use?
Which service depends on it?
NIST specifically recommends a single central inventory to reduce the likelihood of overlooking important certificates. Its recommended inventory data includes SANs, issuing CA, key length, algorithms, expiration, installation location, certificate owner, contacts and approvers.
That means:
You cannot reliably automate what you cannot reliably see.
Is certificate inventory the same as cryptographic inventory?
No.
This is important because your supplied draft starts moving from certificate inventory toward CBOM/PQC.
A certificate inventory focuses on certificates and their associated metadata.
A broader cryptographic inventory can include:
- certificates
- keys
- algorithms
- protocols
- cryptographic libraries
- application dependencies
- cryptographic services
So I would not claim that CLM automatically creates a complete CBOM unless CEMA specifically has that capability and ID Security wants to make that product claim.
Instead say:
Certificate inventory provides an important input into broader cryptographic discovery and crypto-agility initiatives, but certificate inventory and cryptographic inventory are not identical.
→ Cryptographic Discovery: How to Build a PQC Cryptographic Inventory
That avoids overlap and strengthens your existing article cluster.
Why does certificate expiry still cause outages?
Certificate expiration is predictable.
Yet expired certificates continue to create outages because organisations may lack complete inventory, ownership, monitoring or reliable renewal processes.
A certificate can be missed because:
- nobody knows it exists;
- its owner has changed;
- a renewal process failed;
- the certificate renewed but was not correctly deployed;
- monitoring covers one environment but not another.
NIST's guidance specifically combines central inventory with continuous monitoring, notifications, automated enrollment and certificate replacement as part of reducing certificate-related operational risk.
The important relationship is:
Inventory → Monitoring → Renewal → Deployment → Verification
Not simply:
Expiration alert → human fixes certificate
What does full Certificate Lifecycle Management include?
How does CLM support different certificate enrollment protocols?
Modern infrastructure does not use one certificate-enrollment mechanism.
Different environments may use different protocols or integrations:
A CLM platform can provide a common management layer across multiple enrollment methods so that certificates requested through different mechanisms still feed into the same inventory, monitoring and governance model.
→ RELATED: Microsoft AD CS and ACME: How to Automate Certificates for Kubernetes, Linux and DevOps
Why does multi-CA certificate management become difficult?
Large organisations rarely have only one source of certificates.
An environment may contain:
Internal enterprise CAs
Public CAs
Application-specific CAs
Cloud certificate services
Legacy PKI
Without a common management layer, each CA can become another source of certificate information, policy and automation.
The challenge isn't necessarily the number of CAs.
It is maintaining:
one view of certificates + consistent ownership + monitoring + policy + lifecycle control
across them.
How does CLM improve certificate governance?
Automation answers:
“Can this certificate be renewed automatically?”
Governance answers different questions:
“Should it be issued?”
“Who owns it?”
“Who is allowed to request it?”
“Which policy applies?”
“What happened to it throughout its lifecycle?”
A mature CLM approach can bring together:
Role-based access control (RBAC)
Approval workflows
Certificate ownership
Policy enforcement
Audit logging
Reporting
NIST's guidance likewise treats governance, ownership, access control, inventory and lifecycle automation as connected parts of enterprise certificate management.
When are scripts still enough?
This section is very important for credibility.
Scripts can remain a sensible solution when:
- the certificate estate is small;
- the environment is homogeneous;
- certificate ownership is clear;
- renewal processes are simple;
- monitoring is reliable;
- there are few integrations;
- audit requirements are limited.
A script is not automatically a certificate-management problem.
The issue is scale and fragmentation.
When should you move from scripts to Certificate Lifecycle Management?
How does Certificate Lifecycle Management support crypto-agility?
CLM becomes particularly important when certificates need to be changed at scale.
A certificate inventory can help identify certificates using particular:
Issuing CAs · algorithms · key sizes · certificate profiles · validity periods
That supports questions such as:
Where are certificates using cryptographic configurations that need to change?
Which applications will need replacement certificates?
Who owns those certificates?
Can replacements be deployed automatically?
NIST explicitly identifies maintaining certificate inventory and efficient replacement processes as supporting crypto-agility and rapid response to cryptographic incidents. NCCoE
But again, keep the distinction clear:
CLM manages certificate lifecycles.
Cryptographic discovery looks beyond certificates at the wider cryptographic estate.
→ RELATED: Cryptographic Discovery: How to Build a PQC Cryptographic Inventory
→ RELATED: How to Build a PQC Migration Roadmap Your Board Can Approve
How does CEMA approach Certificate Lifecycle Management?
This is where ID Security should enter, not throughout the entire article.
CEMA Certificate Lifecycle Management provides a central layer for managing certificate lifecycles across heterogeneous PKI environments.
The objective is to replace isolated certificate processes with a governed lifecycle that brings together areas such as:
certificate inventory · enrollment · renewal · monitoring · policy · reporting
across different certificate use cases and infrastructure.
This allows organisations to retain the PKI infrastructure appropriate to their environment while centralising certificate lifecycle operations.
→ EXPLORE CEMA CERTIFICATE LIFECYCLE MANAGEMENT
THE KEY TAKEAWAY
Scripts are not inherently the wrong way to manage certificates.
They become a problem when an organisation can no longer answer simple operational questions reliably:
What certificates do we have?
Where are they deployed?
Who owns them?
When do they expire?
Are they compliant with policy?
Will they renew and deploy successfully?
Certificate Lifecycle Management turns those individual certificate processes into a managed operational lifecycle.
And that is the real transition:
from automating certificates individually → to managing certificates systematically.
-
FREQUENTLY ASKED QUESTIONS ABOUT CERTIFICATE LIFECYCLE MANAGEMENT
What is Certificate Lifecycle Management?
Certificate Lifecycle Management (CLM) is the structured management of certificates across processes such as discovery, inventory, enrollment, deployment, monitoring, renewal and revocation.
Why is Certificate Lifecycle Management important?
CLM helps organisations maintain visibility and control over certificates so that expiration, ownership, policy and renewal do not have to be managed independently across different systems.
What is the difference between certificate automation and CLM?
Certificate automation automates individual certificate operations. Certificate Lifecycle Management connects those operations with inventory, monitoring, ownership, policy and governance.
Can scripts be used for certificate management?
Yes. Scripts can be effective for specific certificate tasks and smaller environments. The challenge arises when certificate management becomes fragmented across many scripts, systems, teams and certificate authorities.
What should a certificate inventory contain?
A useful inventory can include certificate identity, SANs, issuer, expiration, installed location, owner, key characteristics and other operational metadata. NIST recommends maintaining an up-to-date central inventory as the foundation of an effective certificate-management program. NCCoE
What is the difference between certificate inventory and cryptographic inventory?
A certificate inventory focuses on certificates and their lifecycle information. A cryptographic inventory is broader and can include keys, algorithms, protocols, cryptographic libraries and dependencies.
Does CLM prevent certificate expiration?
CLM can reduce expiration risk through central inventory, monitoring, alerts and automated renewal processes. No system makes operational failure impossible, so monitoring and verification remain important.
Does CLM work with multiple certificate authorities?
CLM architectures can be designed to manage certificates from multiple issuing CAs through a common inventory, policy and lifecycle-management layer.
How does CLM help with PQC readiness?
Certificate inventory and automated replacement capabilities help organisations identify certificate configurations and replace certificates at scale as cryptographic requirements change. Broader PQC readiness also requires cryptographic discovery beyond certificates.
When should an organisation move from scripts to CLM?
Common indicators include fragmented certificate inventories, recurring expiry incidents, multiple certificate authorities, many independent automation scripts, manual audit reporting and certificate processes dependent on individual engineers.