Google’s 2029 PQC target: What it means for your migration

Google’s 2029 PQC target: What it means for your migration
Google’s 2029 target is a date for its own migration to post-quantum cryptography (PQC). It does not predict when a quantum computer will be able to break today’s public-key cryptography, and it does not set a deadline for your organisation. What it does give you is a reason to ask a more practical question: what needs to change in your environment, and which parts of that change depend on someone else?
If you run a partner-facing API, for example, you might control the gateway and its certificate. Your partner controls the client that still needs to connect. A vendor roadmap can tell you when a feature is planned. It cannot tell you when both sides of that connection will be ready.
What did Google announce for 2029?
In its March 2026 announcement, Google set 2029 as its target for migrating to post-quantum cryptography. It cited developments in quantum hardware, error correction and attack resource estimates. In August, Google Cloud published its own roadmap, targeting PQC readiness by 2029 while anticipating further work in the 2030s.
There are two risks to consider when deciding where to start:
- Confidentiality: An attacker can collect encrypted traffic today and attempt to decrypt it later. Data that must stay confidential for years deserves particular attention.
- Authentication and digital signatures: A future attacker capable of breaking the underlying public-key algorithms could forge signatures or impersonate a service. Replacing those mechanisms takes time, especially where clients, partners and suppliers must upgrade together.
For a migration plan, these are different questions. How long must the data stay confidential? How long will it take to replace the systems you rely on to establish trust? The answers may point to different priorities.
What do quantum attack estimates actually tell us?
Google Research’s March 2026 analysis estimates the resources a quantum computer would need to solve the elliptic curve discrete logarithm problem for a 256-bit curve. That is an estimate for a specific computation under particular assumptions. It does not demonstrate that a machine with those capabilities exists today.
IBM’s November Starling update is a different kind of evidence: an engineering roadmap for a planned fault-tolerant quantum computer. Here is how to read the two together. www.ibm.com
The takeaway is simple: use attack estimates to understand how the risk is changing, and hardware roadmaps to track engineering progress. Neither gives you a reliable date for when the attack becomes practical. Your migration plan still needs to account for how long discovery, procurement and compatibility testing take.
Why does 2029 matter for PKI teams?
Because your suppliers’ plans can affect what you can test and when. Google, Google Cloud and Cloudflare all use 2029 in their published plans, but they describe different scopes. Even where two vendors use the same year, the relevant features may become available in different products, versions or environments.
Ask each critical supplier for the product, version, test availability and compatibility requirements that apply to your use case. “We’re targeting 2029” is useful context. “You can test your gateway and partner client together on these versions” is something you can put on a project plan.
What should Swiss financial institutions take from FINMA’s guidance?
FINMA Guidance 05/2026 on quantum computing puts the emphasis on assessing exposure and preparing a transition. Its published summary highlights an institution-specific risk analysis, a cryptographic inventory, a migration roadmap and the involvement of external service providers. Those are distinct from a technology supplier’s migration target. FINMA
In practice, if a critical service is outsourced, record which provider owns the change, what its plan covers and how your team will verify that the service still works. For the Swiss financial-services perspective, see our analysis of FINMA’s quantum computing guidance. [Internal link: bind to the FINMA article.]
What should you do now? Map one critical service.
Start with a service you know well: a VPN, customer portal or partner API. For each place it uses cryptography, record four things:
- What’s in use? Note the certificate, protocol or algorithm, and where it is used. For a TLS service, start with the issuing CA and the component that terminates TLS.
- Who can change it? Name the owner who can approve the change and the team that can implement it.
- What must keep working? Record the clients, applications, libraries and partner systems that depend on the current setup.
- What would you need to verify? Identify an open question or a test, such as whether a partner’s client can still connect after a configuration change.
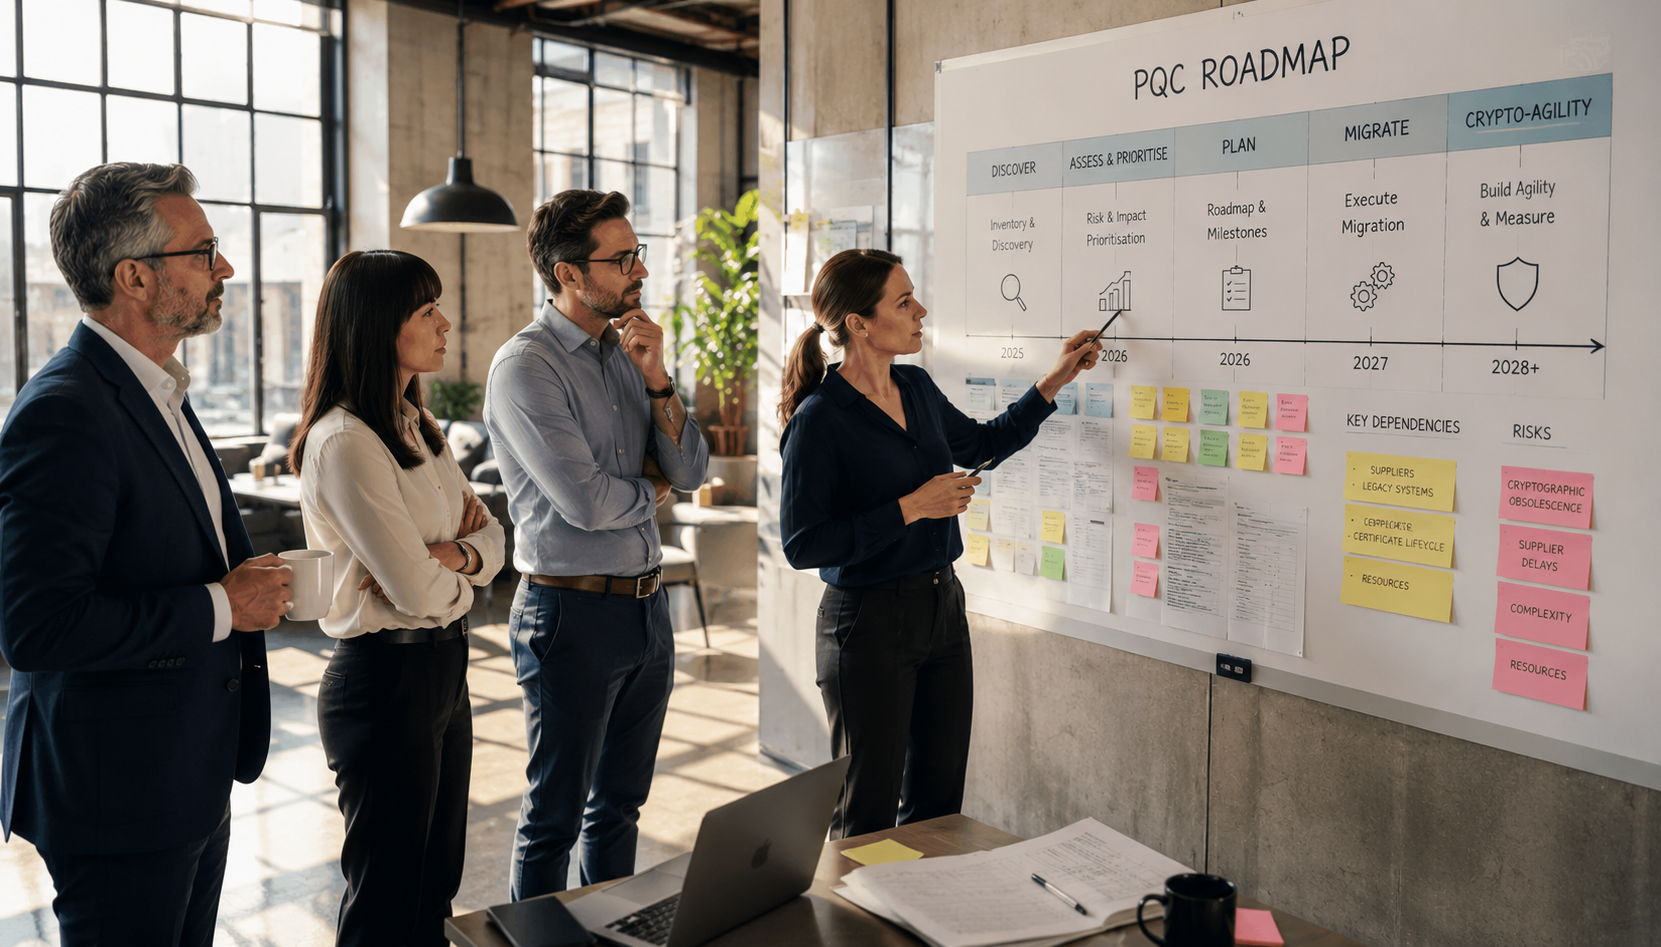
If you can’t name the owner or test the dependency yet, add that gap to your plan. It gives you a concrete next step before you commit to a pilot date.
Our guide to building a PQC cryptographic inventory explains what to capture beyond your certificate inventory. Once you have enough information to set priorities, use our guide to building a PQC migration roadmap your board can approve to turn those findings into decisions.
-
Frequently asked questions
Did Google say quantum computers will break encryption in 2029?
No. Google set 2029 as a target for migrating to post-quantum cryptography. It did not predict when a quantum computer capable of breaking today’s public-key cryptography would exist.
Is 2029 a deadline for every organisation?
No. Google’s date is a vendor target. Set your own milestones based on the sensitivity of your data, the services that must keep working, supplier lead times and any guidance that applies to your organisation.
Where should a team start with PQC migration?
Start with one critical service. Identify where it uses cryptography, who owns each component, and which clients and suppliers depend on it. Use the gaps you find to decide what to investigate or test first.
Is a certificate inventory enough?
A certificate inventory is a useful starting point. A broader cryptographic inventory should also cover where algorithms, keys, protocols and signing or authentication mechanisms are used, including in applications and outsourced services.
What should we ask suppliers about PQC?
Ask which products and versions will support your use case, when you can test them, and which clients or other components must change at the same time. Get a named contact for compatibility testing.