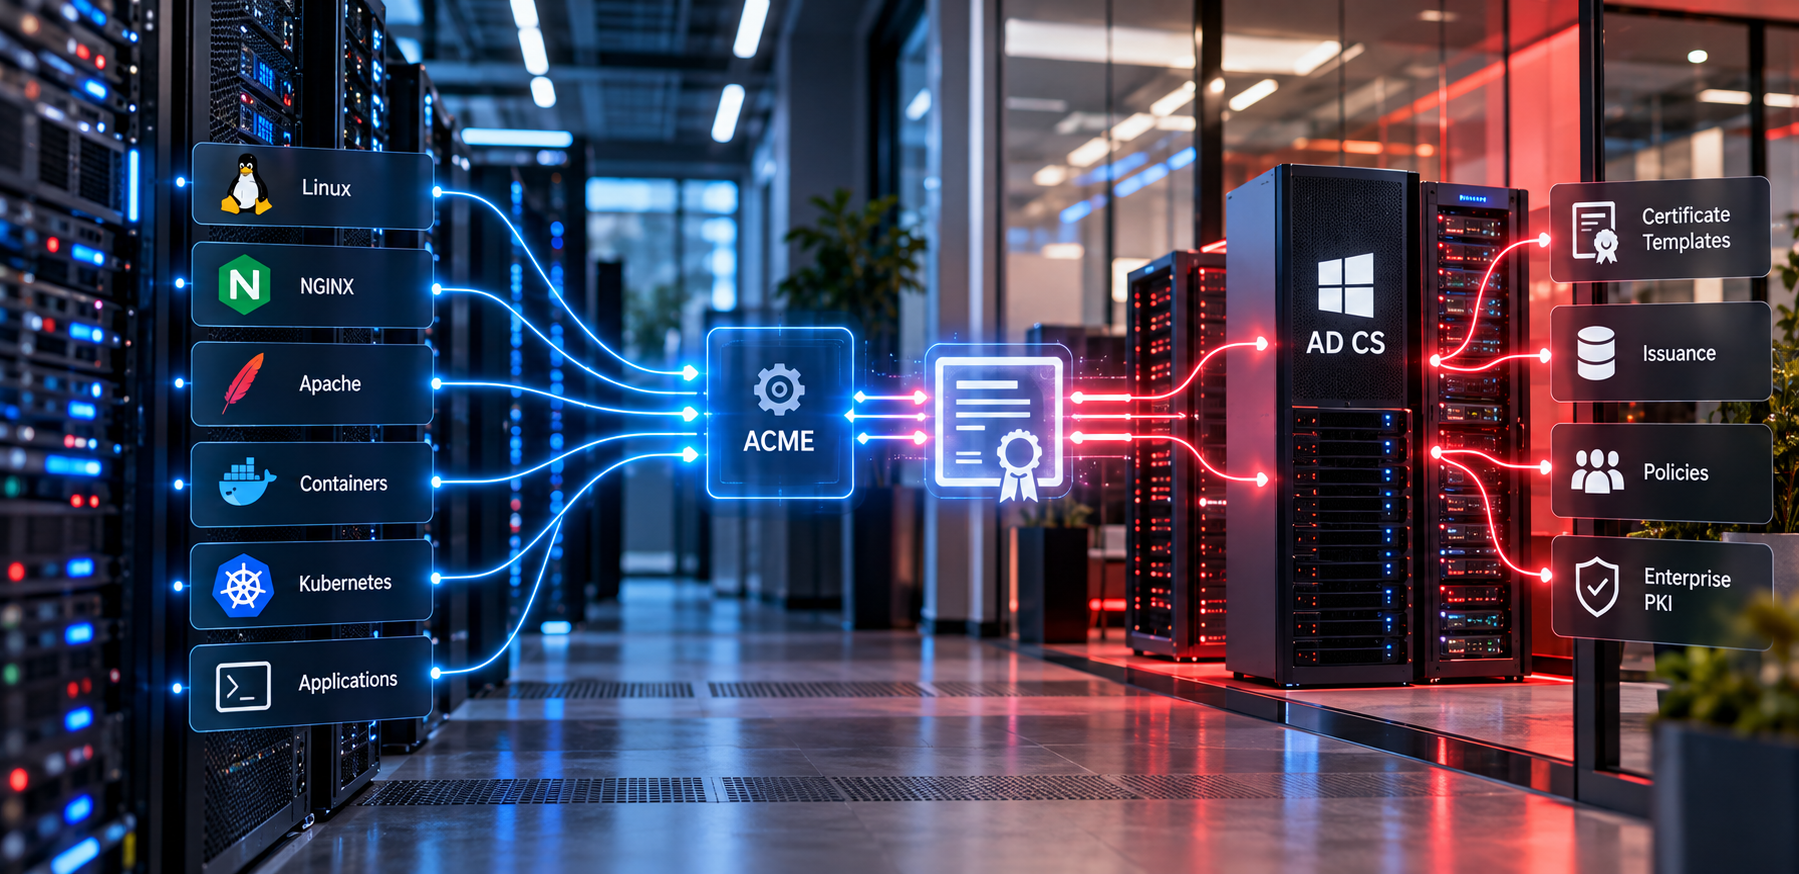
Microsoft AD CS Auto-Enrollment at Scale: Renewal, Templates and Visibility
AD CS AUTO-ENROLLMENT AT A GLANCE
How does Microsoft AD CS auto-enrollment work?
The basic process is straightforward:
Certificate Template → Permissions → Issuing CA → Group Policy → User or Computer → Certificate
Certificate templates define how certificates should be requested, issued and used.
Enterprise certificate templates are stored in Active Directory Domain Services (AD DS) and can be made available to enterprise CAs across the forest. Microsoft Learn
Administrators configure which users or computers have permission to read, enroll and auto-enroll for the appropriate certificate.
Windows then handles the enrollment process automatically according to the configured policy.
For large Windows fleets, this removes a significant amount of manual certificate work.
But automating enrollment is not the same as managing the complete certificate lifecycle.
When does AD CS renew a certificate?
AD CS auto-enrollment does not simply renew every certificate when it reaches 80% of its lifetime.
Microsoft documents two conditions for normal renewal:
- The certificate must have completed at least 80% of its validity period.
- The certificate must be within the renewal period configured in the certificate template.
For example, Microsoft explains that a one-year certificate with a six-week renewal period reaches 80% of its lifetime earlier, but renewal occurs once it enters the six-week renewal window.
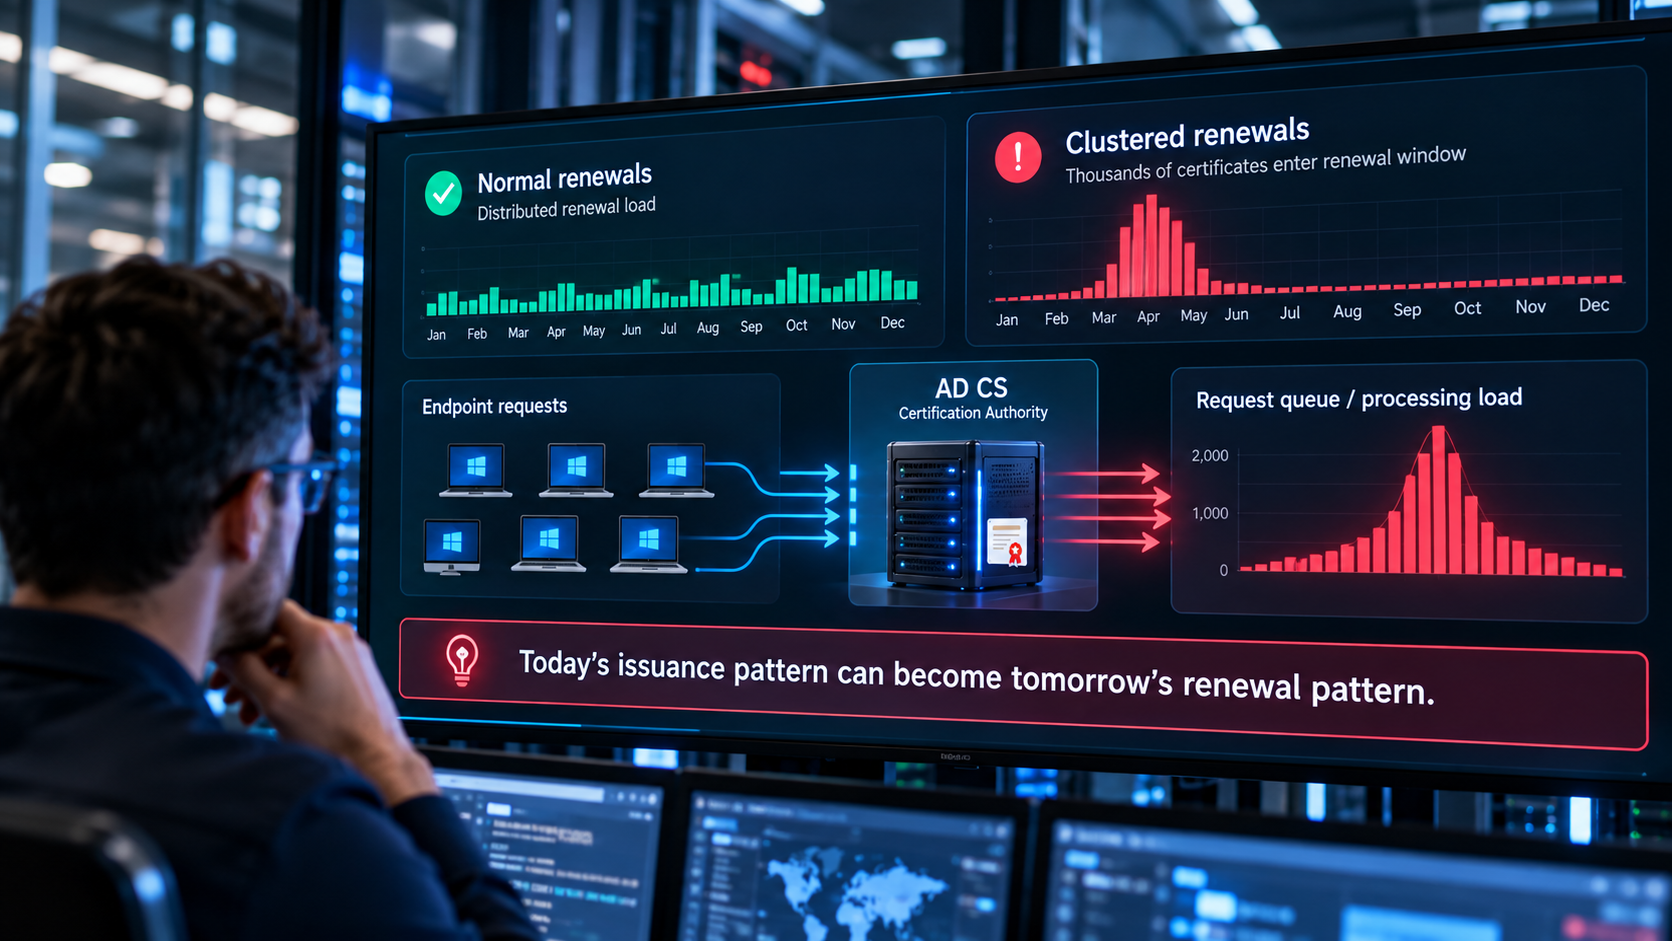
What happens when many certificates renew at the same time?
Imagine that thousands of endpoints receive certificates during the same deployment period.
Those certificates may also approach their renewal windows during a similar period later.
This can create a concentrated renewal wave.
The operational impact depends on factors such as:
- number of certificates;
- renewal-window configuration;
- CA capacity;
- enrollment architecture;
- client availability;
- retry behaviour.
The point is not that a large fleet automatically overwhelms AD CS.
It is that:
A concentrated issuance pattern can later become a concentrated renewal pattern.
At scale, certificate renewal therefore becomes something worth monitoring, rather than simply assuming it is happening in the background.
How do AD CS certificate templates work?
Certificate templates define the rules and settings used when certificates are requested and issued.
They can control areas such as certificate purpose, permissions, validity settings and cryptographic configuration.
Microsoft supports several certificate-template versions. Version 2 templates introduced configurable certificate auto-enrollment, while later versions extend those capabilities.
Templates are therefore central to AD CS automation.
But they also introduce an important operational question:
When certificate policy changes, how do you verify that the intended certificate state has reached the intended endpoints?
What happens when an AD CS certificate template changes?
This needs more careful wording than the original draft.
Changing certificate requirements does not mean that every existing certificate across the fleet is immediately replaced.
Administrators may duplicate or modify templates, publish templates to issuing CAs and use mechanisms such as template supersedence when a newer template should replace an older enrollment configuration.
For example:
Existing template
Workstation-v1
↓
New security requirement
↓
Replacement template
Workstation-v2
↓
Supersede v1
↓
Eligible clients enroll using v2
Microsoft documents superseded-template relationships and notes that they must be maintained when relevant template objects are changed or renamed.
The operational challenge is therefore not simply creating the new template.
It is verifying the result.
What is certificate template supersedence?
Certificate template supersedence allows a newer template to replace one or more older templates for certificate enrollment.
A superseding template can be configured with older templates listed under Superseded Templates and then published to the appropriate CA. Microsoft uses this mechanism in its own Windows deployment guidance. Microsoft Learn
Simple example
At small scale, administrators can investigate individual endpoints when necessary.
At large scale, the more important question becomes:
How many certificates are still associated with the previous certificate configuration?
Why does template governance matter?
Suppose a security requirement changes and a new certificate configuration must be deployed across thousands of endpoints.
Publishing the appropriate template is one part of the process.
Operations may also need to know:
Which endpoints received the expected certificate?
Which certificates still reflect the previous configuration?
Which enrollment attempts failed?
Which systems have not recently connected?
Where is remediation required?
That creates an important distinction:
Configuration defines the intended state.
Lifecycle visibility shows the actual state.
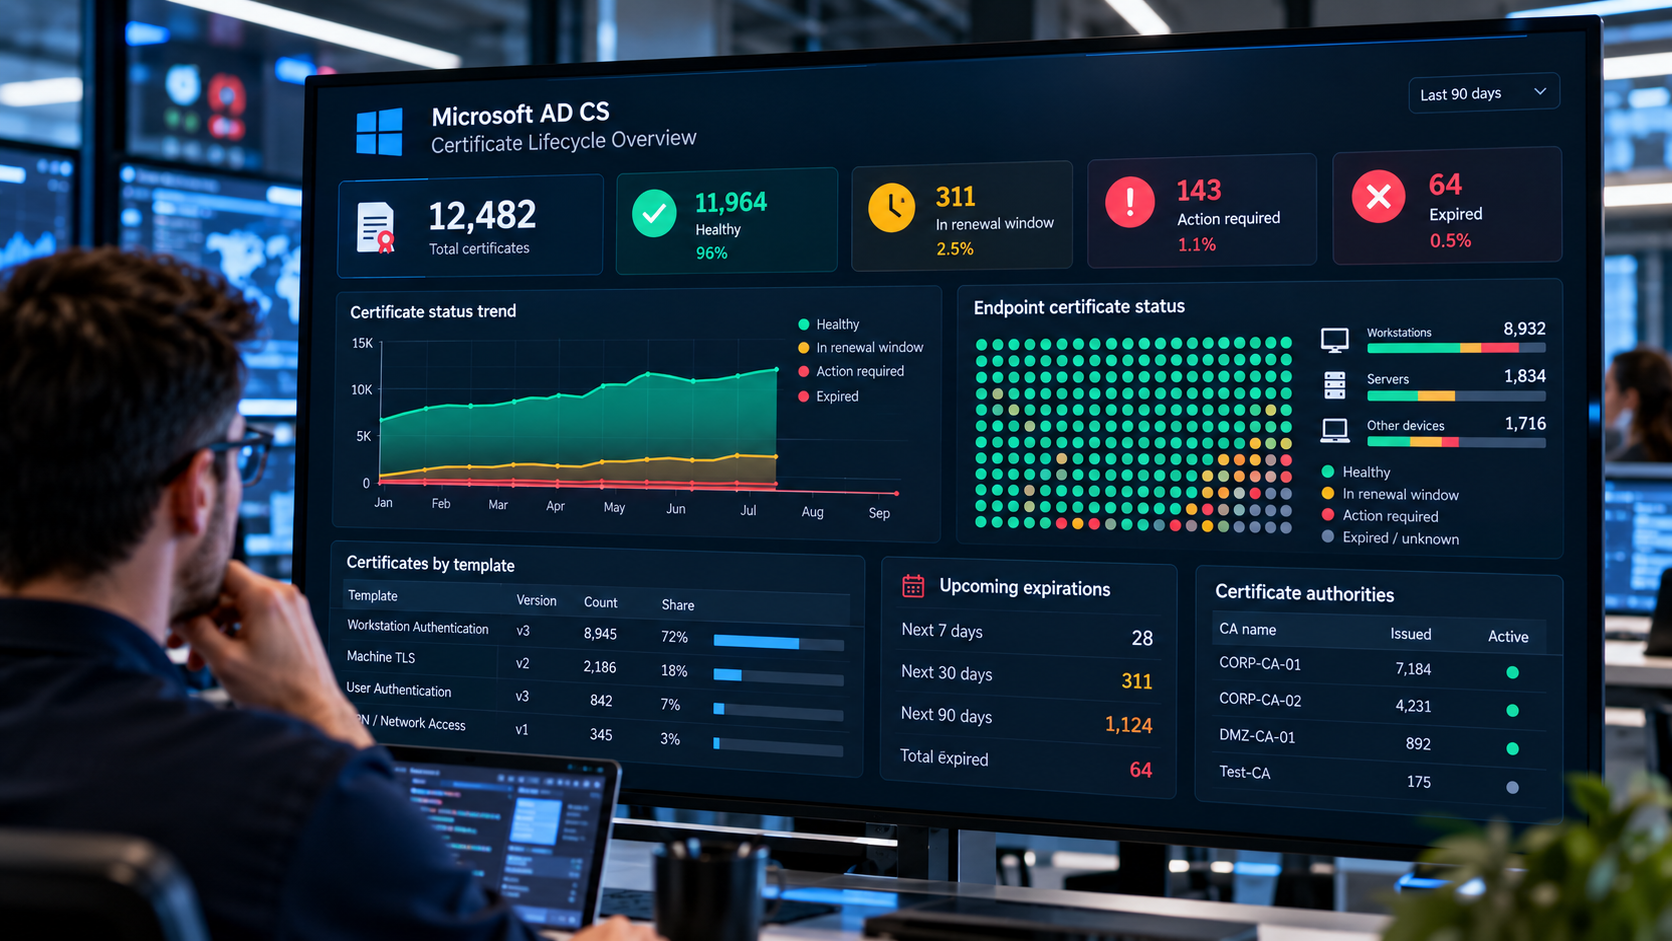
What visibility does AD CS provide?
AD CS provides administrative tools and certificate data for managing the certification authority and its issued certificates.
Microsoft's certificate-template tools allow administrators to view and manage templates, permissions and issuance configuration.
That is different from having a dedicated Certificate Lifecycle Management dashboard built around fleet-wide operational questions.
For example:
- What expires in the next 30 days?
- Which certificates successfully renewed?
- Which certificates require attention?
- Which certificate configurations are still in circulation?
- Which CA issued each certificate?
- Which service or team owns it?
As the certificate estate grows, answering those questions quickly becomes increasingly important.
AD CS vs Certificate Lifecycle Management
What are the common auto-enrollment challenges at scale?
When is AD CS auto-enrollment enough?
This section is important because we don't want the article to imply:
“Large environment = AD CS bad.”
That's not accurate.
AD CS auto-enrollment can remain highly effective when the organisation is predominantly Windows-based and has sufficient operational controls around its certificate estate.
The key questions are:
Do we know what certificates exist?
Can we see what is approaching expiration?
Can we verify renewals?
Can we track certificate-policy changes?
Can we identify problems quickly?
If the answer is yes, endpoint count alone is not a reason to introduce another platform.
There is no universal endpoint number at which AD CS auto-enrollment stops working.
The trigger is usually operational complexity, not a specific fleet size.
When should you add a CLM layer above AD CS?
How does CEMA complement Microsoft AD CS?
CEMA does not need to replace Microsoft AD CS.
AD CS can remain the certificate authority and Windows enrollment infrastructure, while CEMA provides the Certificate Lifecycle Management layer around it.
This can give organisations a central view of certificate inventory, renewal status, monitoring, reporting and lifecycle operations.
The architecture becomes:
Windows endpoints
↓
AD CS auto-enrollment
↓
Microsoft AD CS
↕
CEMA Certificate Lifecycle Management
↓
Inventory · Monitoring · Automation · Governance · Reporting
The goal is not to replace a certificate-enrollment mechanism that already works.
It is to add the operational visibility and lifecycle management needed around it.
CEMA can be deployed as SaaS, dedicated managed service, hybrid or on-premises, depending on organisational requirements.
How does this connect to certificate lifecycle management?
AD CS auto-enrollment is one part of a broader certificate-management architecture.
Other environments may use different enrollment mechanisms:
A Certificate Lifecycle Management layer can bring these different certificate populations into a common operational view.
RELATED INSIGHTS
→ Certificate Lifecycle Management: When Scripts Are No Longer Enough
→ IIS, SNI, and Multi-SAN Certificates: Where AD CS Auto-Enrollment Runs Out of Runway
→ Microsoft AD CS and ACME: How to Automate Certificates for Kubernetes, Linux and DevOps
THE KEY TAKEAWAY
AD CS auto-enrollment solves an important problem extremely well:
Automatically enrolling and renewing certificates for eligible Windows users and computers.
But enrollment is only one part of the certificate lifecycle.
As certificate estates become larger and more complex, organisations increasingly need to understand:
What is enrolled?
What is renewing?
What is expiring?
Which certificate configurations are still in use?
Did the latest policy change reach the intended fleet?
Where is intervention required?
That is the difference between certificate auto-enrollment and Certificate Lifecycle Management.
-
FREQUENTLY ASKED QUESTIONS ABOUT AD CS AUTO-ENROLLMENT
What is AD CS auto-enrollment?
Microsoft AD CS auto-enrollment allows eligible Windows users and computers to automatically request and renew certificates according to certificate templates and policy. Version 2 and later certificate templates support auto-enrollment.
When does AD CS renew certificates?
For normal renewal, Microsoft states that a certificate must have completed at least 80% of its validity period and be within the renewal period configured in the certificate template.
How often does certificate auto-enrollment run?
Microsoft states that certificate auto-enrollment runs every eight hours in its current renewal guidance.
What is an AD CS certificate template?
A certificate template contains rules and settings that define how a certificate should be requested, issued and used. Enterprise certificate templates are stored in AD DS.
What is certificate template supersedence?
Template supersedence allows a newer certificate template to supersede one or more older templates. Microsoft documents the Superseded Templates configuration as part of certificate-template management and Windows certificate deployments.
Does changing a certificate template automatically replace every certificate?
Not necessarily. The result depends on the change and enrollment configuration. Where a replacement template is intended to supersede an older template, the supersedence relationship must be configured and the relevant template published.
What is an AD CS renewal storm?
“Renewal storm” is an operational term for a concentrated period of certificate-renewal activity. The impact depends on the size and distribution of the certificate population, renewal settings and CA architecture.
Is AD CS suitable for large environments?
There is no universal endpoint threshold at which AD CS auto-enrollment becomes unsuitable. The important factors are architecture, capacity, monitoring, certificate visibility and operational complexity.
Does CLM replace Microsoft AD CS?
Not necessarily. AD CS can remain the issuing CA and Windows enrollment infrastructure while a CLM platform adds central inventory, monitoring, automation, governance and reporting.
What does CLM add to AD CS?
CLM adds an operational management layer around certificates, helping organisations monitor certificate state and lifecycle processes across larger and more heterogeneous environments.