CipherMail 6.3.5: Lower Memory Usage, Faster CRL Checks and New Company Portal
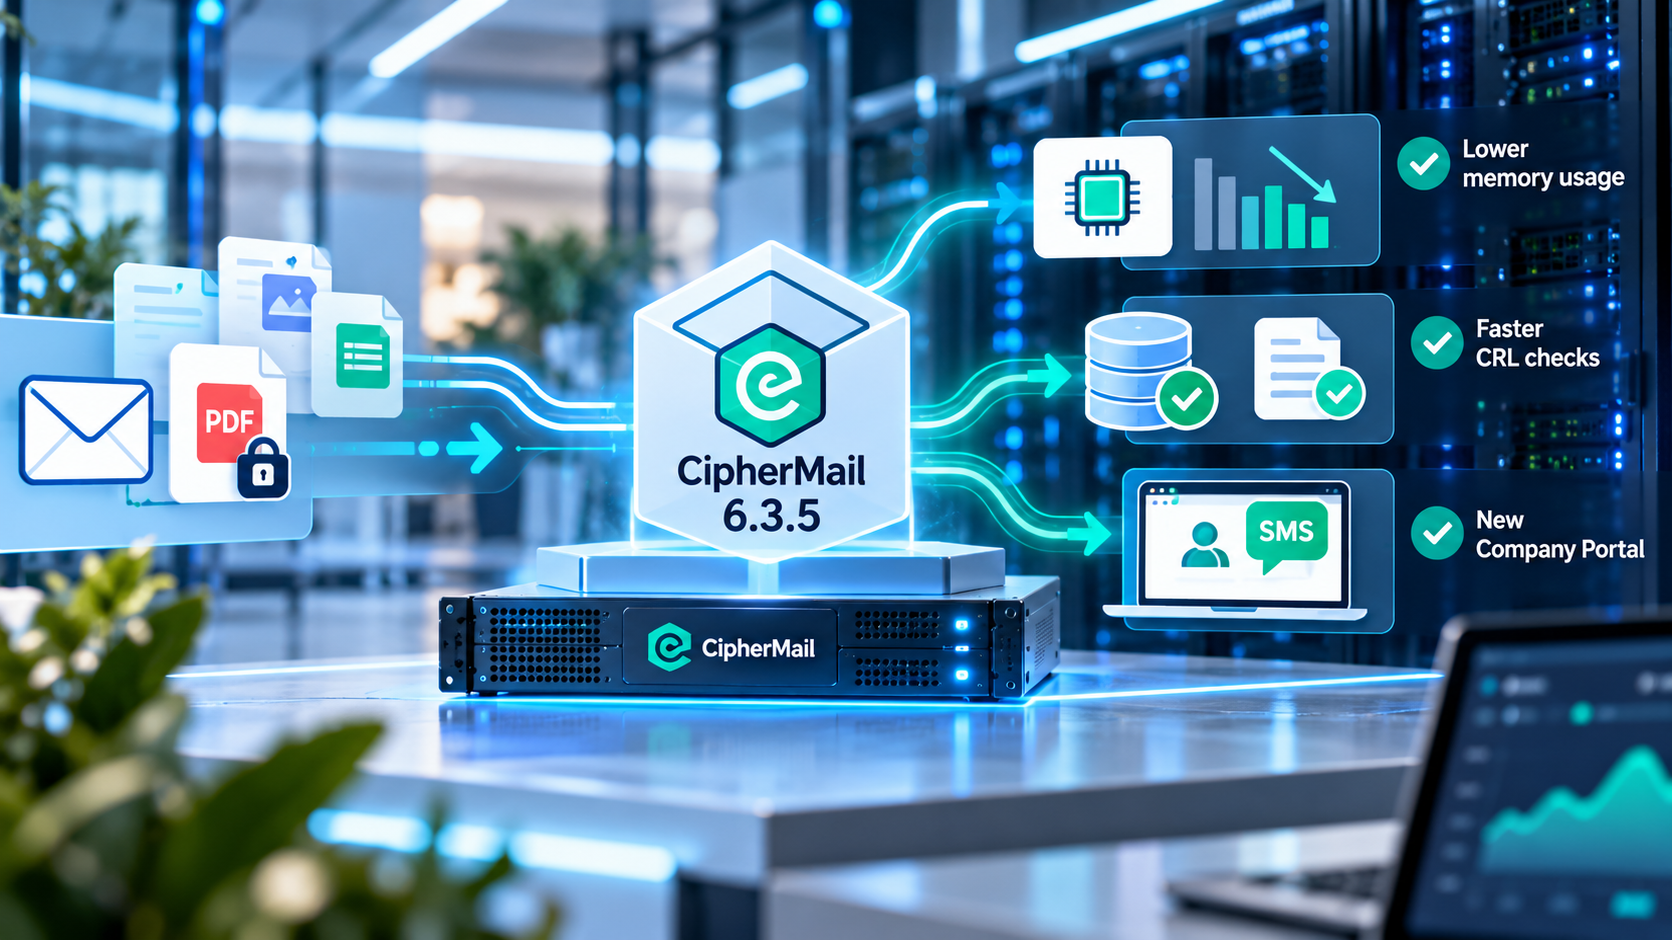
CipherMail 6.3.5: lower memory usage, faster CRL checks and new company portal
How can organisations improve secure email gateway performance without compromising certificate validation or email security?
Released on 14 September 2026, CipherMail Secure Email Gateway 6.3.5 introduces important improvements to memory management, certificate revocation checking and secure email workflows.
The update reduces memory consumption during message processing, introduces more efficient Certificate Revocation List (CRL) caching, adds a new Company Portal for internal users and addresses security vulnerabilities.
For IT administrators managing S/MIME encryption, digital signatures and certificate validation, these changes can help reduce infrastructure overhead and simplify day-to-day operations.
What's new in CipherMail 6.3.5?
CipherMail 6.3.5 focuses on four key areas:
- Lower memory consumption: Large emails are streamed from temporary files instead of being held entirely in memory.
- Faster certificate revocation checking: CRLs are decoded and verified once, with certificate-chain validation results cached for reuse.
- New Company Portal: Internal users can send SMS messages to external recipients, supporting secure PDF password delivery workflows.
- Security improvements: Updated dependencies, a hostname verification fix and additional limits on resource-intensive message processing.
These improvements are particularly relevant for organisations processing large email volumes, managing extensive PKI environments or operating CipherMail in virtualised infrastructure.
1. Reduced memory usage for S/MIME email processing
Email encryption gateways process messages through multiple security operations, including encryption, decryption, digital signing and certificate validation.
When messages contain large attachments, memory consumption can increase significantly, especially when multiple messages are processed simultaneously.
CipherMail 6.3.5 reduces memory consumption by streaming larger messages from temporary files instead of keeping their complete contents in memory.
How does CipherMail 6.3.5 reduce memory consumption?
In previous versions, processing a large message could consume several times the message's original size in memory for each spool thread.
Version 6.3.5 changes how messages are handled.
Messages larger than 1 MB are stored temporarily and processed as streams rather than being held entirely in the Java heap.
Administrators can configure the threshold using:
ciphermail.message.memory-threshold
This approach applies across several CipherMail operations:
- Email queue processing
- S/MIME encryption and decryption
- S/MIME digital signatures
- PDF encryption
- DKIM signing
- IMAP client processing
- Webmail downloads
By reducing the amount of memory allocated to each message, CipherMail can process large emails more efficiently.
What does this mean for virtual machines?
Lower memory requirements can make it easier to operate secure email gateways in virtualised environments.
In tests described in the source material, a standard CipherMail gateway without Webmail Messenger, the PDF Portal or Company Portal operated successfully with 2 GB of memory.
However, the CipherMail 6 performance whitepaper recommends 8–16 GB per node for production environments.
The 2 GB test result should therefore not be interpreted as a universal production sizing recommendation.
Actual memory requirements depend on message volumes, enabled services, concurrency and deployment architecture.
For administrators, the main benefit is greater flexibility when sizing virtual machines and allocating gateway resources.

2. Faster certificate revocation checking with CRL caching
Certificate validation is essential for secure S/MIME communication.
Before trusting a certificate, an email encryption gateway must determine whether it remains valid and whether the issuing certificate authority has revoked it.
One common mechanism is a Certificate Revocation List (CRL), a digitally signed list of revoked certificates published by a certificate authority.
In environments with large CRLs, repeatedly processing these lists can consume substantial memory and processing time.
How does CRL caching work in CipherMail 6.3.5?
CipherMail 6.3.5 introduces more efficient certificate revocation processing.
Instead of decoding a CRL and verifying its signature separately for every certificate check, the gateway:
- Downloads the relevant CRL.
- Decodes the CRL and verifies its signature.
- Keeps the decoded CRL in memory for subsequent checks.
- Caches the revocation status of certificate chains that have already been validated.
By default, the certificate-chain revocation cache supports up to 10,000 entries.
This reduces repeated processing when certificates are checked multiple times.
Performance improvements for large CRLs
The manufacturer's performance measurements illustrate why this matters.
In the previous processing approach, checking a certificate against a CRL containing approximately one million revoked certificates required:
- 46.7 MB: CRL file size
- 1,526 ms: Time for one certificate check
- 1.7 GB: Memory allocated during the operation
These are measurements of the previous approach, not measured performance figures for the new cache.
CipherMail 6.3.5 reduces redundant work by reusing decoded CRLs and cached validation results.
Improved CRL handling in clustered environments
The improvements also extend to CipherMail clusters.
Previously, individual cluster nodes could independently download the same revocation lists.
With CipherMail 6.3.5, only one node downloads the CRLs, reducing duplicated downloads across the cluster.
This can be particularly valuable for organisations operating multiple gateways or working with certificate authorities that publish large revocation lists.
How to inspect or clear the CRL cache
Administrators can inspect the CRL cache using the CipherMail command-line interface.
View cache statistics:
ciphermail-cli crl cache-statistics
Invalidate the cache:
ciphermail-cli crl invalidate-caches
The cache can also be managed through the administration console.
The first command displays cache information without modifying it. The second invalidates cached entries.
Administrators should use cache invalidation deliberately because subsequent certificate checks may require additional processing.
[INSERT HTML CALLOUT — CipherMail CRL Cache Commands]
Show the two commands in a dark navy code panel, with a short explanation of what each command does.
3. New CipherMail company portal for secure password delivery
CipherMail 6.3.5 introduces the Company Portal, a web interface designed for an organisation's internal users.
Unlike the existing CipherMail Portal for external recipients, the Company Portal supports workflows initiated by employees within the organisation.
Its primary use case is the secure delivery of passwords associated with encrypted PDF documents.
How does the Company Portal work?
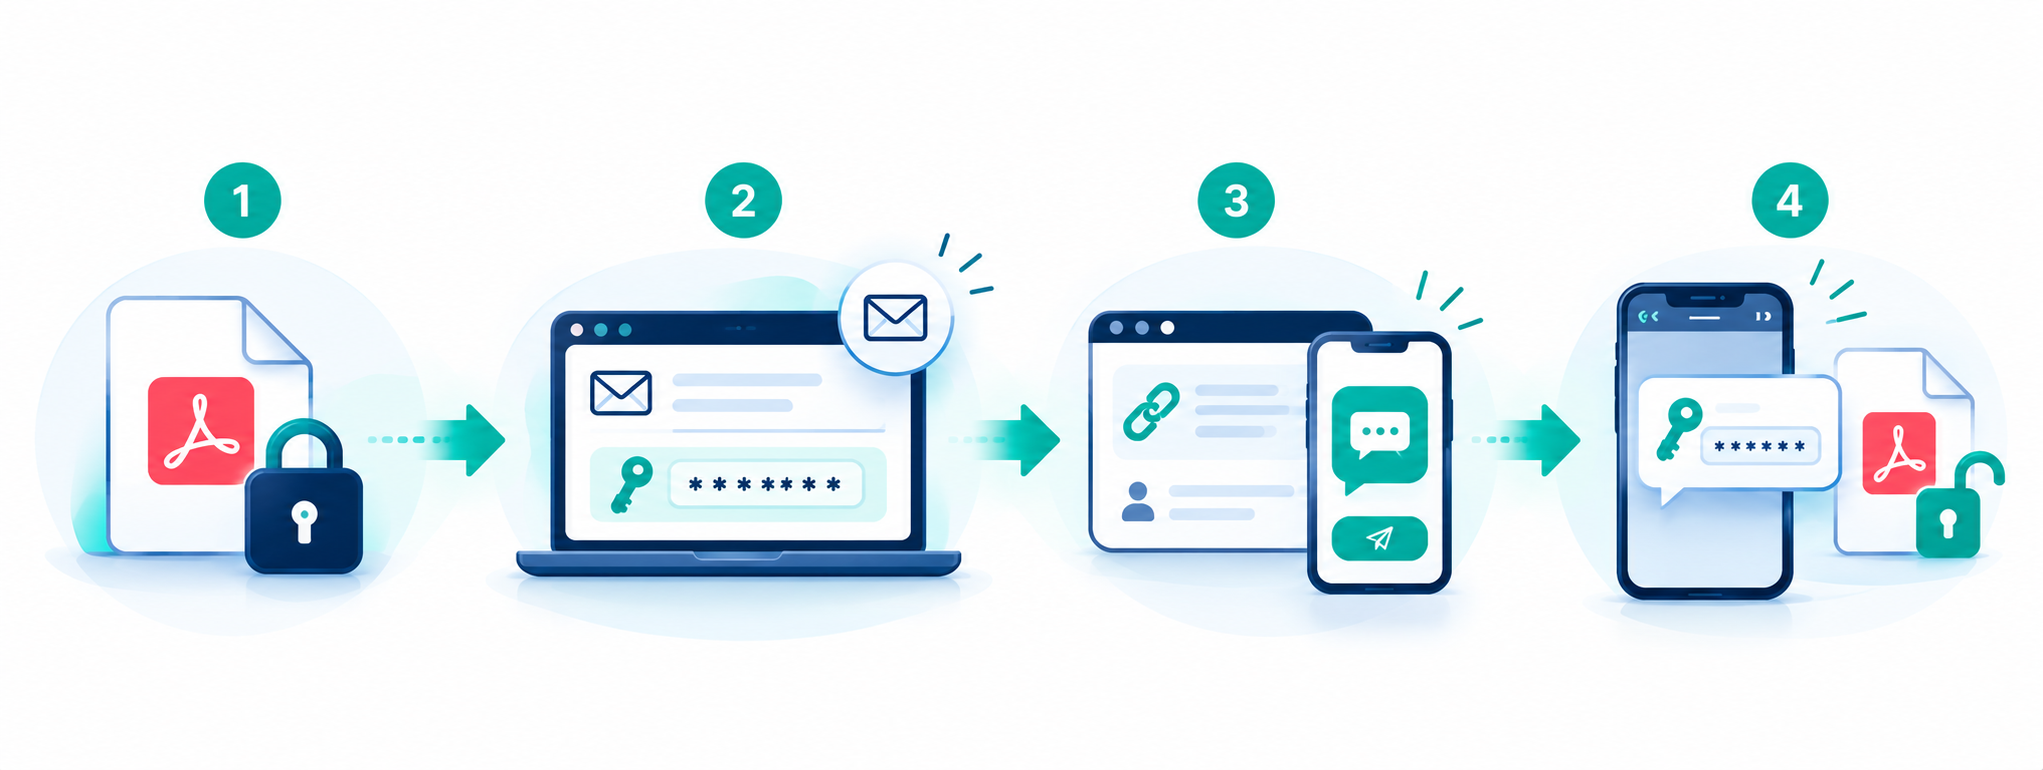
CipherMail supports a PDF encryption workflow called Send Generated Password Back to Sender.
In this configuration, the gateway generates a password for an encrypted PDF and sends the password back to the original sender.
The sender can then communicate that password to the intended recipient through a separate channel.
With the new Company Portal, the process becomes easier.
- CipherMail encrypts a PDF and generates a password.
- The gateway sends the generated password back to the sender.
- The notification email can include a link for each recipient.
- The sender opens the Company Portal using the link.
- The recipient's email address is pre-filled in the SMS dialog.
- The sender can send an SMS containing the password through the configured SMS transport.
Recipient telephone numbers can be retrieved from a personal address book or a company address book maintained by the administrator.
This workflow helps employees distribute passwords without manually switching between unrelated tools.
Why use SMS for encrypted PDF passwords?
Sending an encrypted document and its password through separate communication channels can reduce the risk associated with transmitting both through the same email.
The Company Portal supports this separation by providing an SMS workflow for password delivery.
However, SMS security depends on the telecommunications infrastructure, device access and the organisation's security policies.
It should not be considered equivalent to end-to-end encrypted messaging.
4. CipherMail company portal configuration and access
The Company Portal is available in CipherMail 6.3.5 but is disabled by default.
Administrators must enable and configure it before employees can use the SMS functionality.
Company Portal configuration requirements
The portal operates on port 8444 and can be enabled at different levels:
- Globally
- Per domain
- Per user
Supported authentication options include:
- Username and password
- LDAP authentication
- Microsoft Entra ID using OpenID Connect (OIDC)
An active SMS transport is required to send messages.
Important security consideration: Restrict access to port 8444
If the CipherMail gateway is accessible from the internet, the manufacturer recommends restricting access to the Company Portal through firewall rules.
Access to port 8444 should be limited to the internal network or a VPN where appropriate.
This helps reduce unnecessary exposure of the portal's authentication interface.
Administrators should also review access permissions and authentication settings before enabling the service.
5. Security fixes in CipherMail 6.3.5
In addition to performance and usability improvements, CipherMail 6.3.5 addresses several security issues.
CVE-2026-71290: Hostname verification
The release fixes CVE-2026-71290, a vulnerability affecting hostname verification behaviour in the asynchronous Apache HttpClient.
According to the release information, the configured hostname verification policy previously had no effect on the asynchronous client.
CipherMail 6.3.5 updates Apache HttpClient to version 5.6.4.
This fix is relevant because hostname verification is an important part of establishing trusted TLS connections.
Additional message-processing protections
CipherMail 6.3.5 also introduces resource limits intended to prevent individual incoming messages from consuming excessive gateway resources.
These include:
- A maximum of 100 S/MIME parts per message.
- Limits on resources consumed when importing certificates from emails.
- Updated software dependencies.
These protections help administrators manage the security and stability of their email processing environment.
6. What administrators should check before upgrading
Although CipherMail 6.3.5 improves memory management, administrators should review existing gateway settings before and after upgrading.
Two default resource settings change in this release.
Spool threads
The default number of spool threads is reduced to 5.
This matters because total memory consumption depends partly on the number of messages being processed concurrently.
Backend memory allocation
The default maximum backend memory allocation changes from 50% to 40%.
The change reserves memory for the Company Portal, which is allocated 10%.
Administrators should compare these defaults with their existing configuration and operational requirements.
CipherMail 6.3.5 upgrade checklist
[INSERT HTML CHECKLIST — CipherMail 6.3.5 Upgrade]
- Confirm the installed CipherMail version.
- Review available gateway memory and resource allocation.
- Check the spool thread configuration.
- Review the backend memory allocation.
- Evaluate the new message streaming threshold.
- Review certificate revocation checking and CRL caching.
- Confirm whether the Company Portal is required.
- Configure authentication and SMS transport if enabling the Company Portal.
- Restrict port 8444 to appropriate networks.
- Review security fixes and test key S/MIME workflows.
- Verify gateway behaviour after the update.
How to update CipherMail
Updates are distributed through the CipherMail update server.
For installations using the supported package-management workflow, administrators can install available updates using:
dnf update
Follow your organisation's normal change-management process, including backups, maintenance planning and post-update validation.
The complete release information is available in the CipherMail Gateway Release Notes.
7. What CipherMail 6.3.5 means for enterprise email security
CipherMail 6.3.5 addresses several operational challenges commonly associated with enterprise email encryption.
Infrastructure efficiency: Streaming larger messages can reduce memory pressure and provide more flexibility when sizing gateway infrastructure.
PKI performance: CRL caching avoids repeated decoding and verification of large certificate revocation lists.
Secure document workflows: The Company Portal simplifies SMS-based password delivery for encrypted PDFs.
Security maintenance: Hostname verification fixes, message-processing limits and updated dependencies strengthen the gateway's security controls.
Together, these improvements make CipherMail 6.3.5 an important maintenance release for organisations relying on centrally managed S/MIME encryption and secure email communication.
8. Simplify secure email management with CipherMail
Managing enterprise email security involves more than encrypting individual messages.
Organisations also need reliable certificate validation, scalable message processing, secure document delivery and consistent security policies.
The CipherMail Secure Email Gateway brings these functions together in a centrally managed solution.
Frequently Asked Questions About CipherMail 6.3.5
What is new in CipherMail 6.3.5?
CipherMail 6.3.5 introduces lower memory usage, improved CRL caching, a new Company Portal and security fixes. The release focuses on improving secure email gateway performance and simplifying administrative workflows.
How does CipherMail 6.3.5 reduce memory consumption?
Messages larger than 1 MB are processed using temporary files and streaming instead of being held entirely in memory. This reduces memory pressure during operations such as S/MIME encryption, decryption and email processing.
What is CRL caching in CipherMail?
CRL caching allows CipherMail to reuse decoded Certificate Revocation Lists and previously checked certificate-chain revocation results. This reduces repeated processing during certificate validation.
How many certificate revocation results can CipherMail cache?
CipherMail 6.3.5 caches certificate-chain revocation status information, with a default capacity of up to 10,000 entries.
What is the CipherMail Company Portal?
The Company Portal is a web interface for internal users. It supports sending SMS messages to external recipients, particularly for delivering passwords generated during encrypted PDF workflows.
Is the CipherMail Company Portal enabled by default?
No. The Company Portal is disabled by default. Administrators must enable it and configure authentication, access permissions and an active SMS transport.
What port does the CipherMail Company Portal use?
The Company Portal uses port 8444. The manufacturer recommends restricting access to internal networks or a VPN when the gateway is internet-accessible.
What security vulnerability does CipherMail 6.3.5 fix?
CipherMail 6.3.5 fixes CVE-2026-71290, involving hostname verification behaviour in the asynchronous Apache HttpClient. The release also updates dependencies and adds limits to resource-intensive message processing.
Can CipherMail 6.3.5 run with less memory?
The release reduces memory consumption. The source material reports a standard gateway operating successfully with 2 GB in testing, but the CipherMail 6 performance whitepaper recommends 8–16 GB per production node. Actual requirements depend on the deployment.
How do I upgrade to CipherMail 6.3.5?
Updates are available through the CipherMail update server and can be installed using the supported package-management process, including dnf update. Administrators should review resource settings and test their environment after upgrading.
Explore CipherMail Secure Email Gateway
From automated S/MIME encryption and certificate validation to secure PDF delivery, CipherMail helps organisations manage sensitive email communication centrally.
Technical References
- CipherMail Gateway Release Notes — Version 6.3.5, released 14 September 2026.
- CipherMail Gateway Administration Guide — Company Portal.
- CipherMail 6 Performance Whitepaper — CipherMail_6_Performance_EN_DE_v1.0.